Category: General IT

  • Is It Time to Pull Your Data Out of the Cloud?

    For years now we have bought into the idea that everything belongs in the public cloud. Spin it up, let someone else worry about the hardware, job done.

    Lately though, I’ve noticed a lot of businesses quietly doing the opposite. They’re pulling their data and applications back onto their own kit.

    There’s a name for it: cloud repatriation. All that means is moving stuff off someone else’s servers and back onto hardware you own and control.

    It’s got me wondering if a lot of us jumped into the cloud a bit too fast.

    Why People Are Having Second Thoughts

    Here’s what I keep hearing from folks who are reconsidering:

    • The bill shock. Cloud costs can spiral fast. Data transfer fees and storage add-ons creep up on you every month.
    • Steady workloads. If you’re running servers 24/7 with predictable traffic, buying your own hardware is often cheaper over a few years.
    • Data control. Keeping your data on your own network makes privacy and compliance rules a lot easier to satisfy.
    • Speed. Local hardware means lower latency and faster response times for everyday tasks.

    Not an All or Nothing Choice

    I’m not saying ditch the cloud completely. For most setups, a hybrid approach, some things kept local and some left in the cloud, is the real sweet spot.

    But hardware has become so efficient lately that owning your own kit makes more sense than it has in years.

    So what’s your take? Are you sticking with the cloud all the way, or are you starting to bring things back in-house?

  • How Windows updates should be managed on a business network

    How Windows updates should be managed on a business network

    Windows updates have a bad reputation. Most people picture the same thing: a machine that reboots itself halfway through a piece of work, or the update that lands on a Friday and breaks something by Monday.

    That reputation is fair. Left alone, PCs update whenever they like. Multiply that across a company and you get chaos.

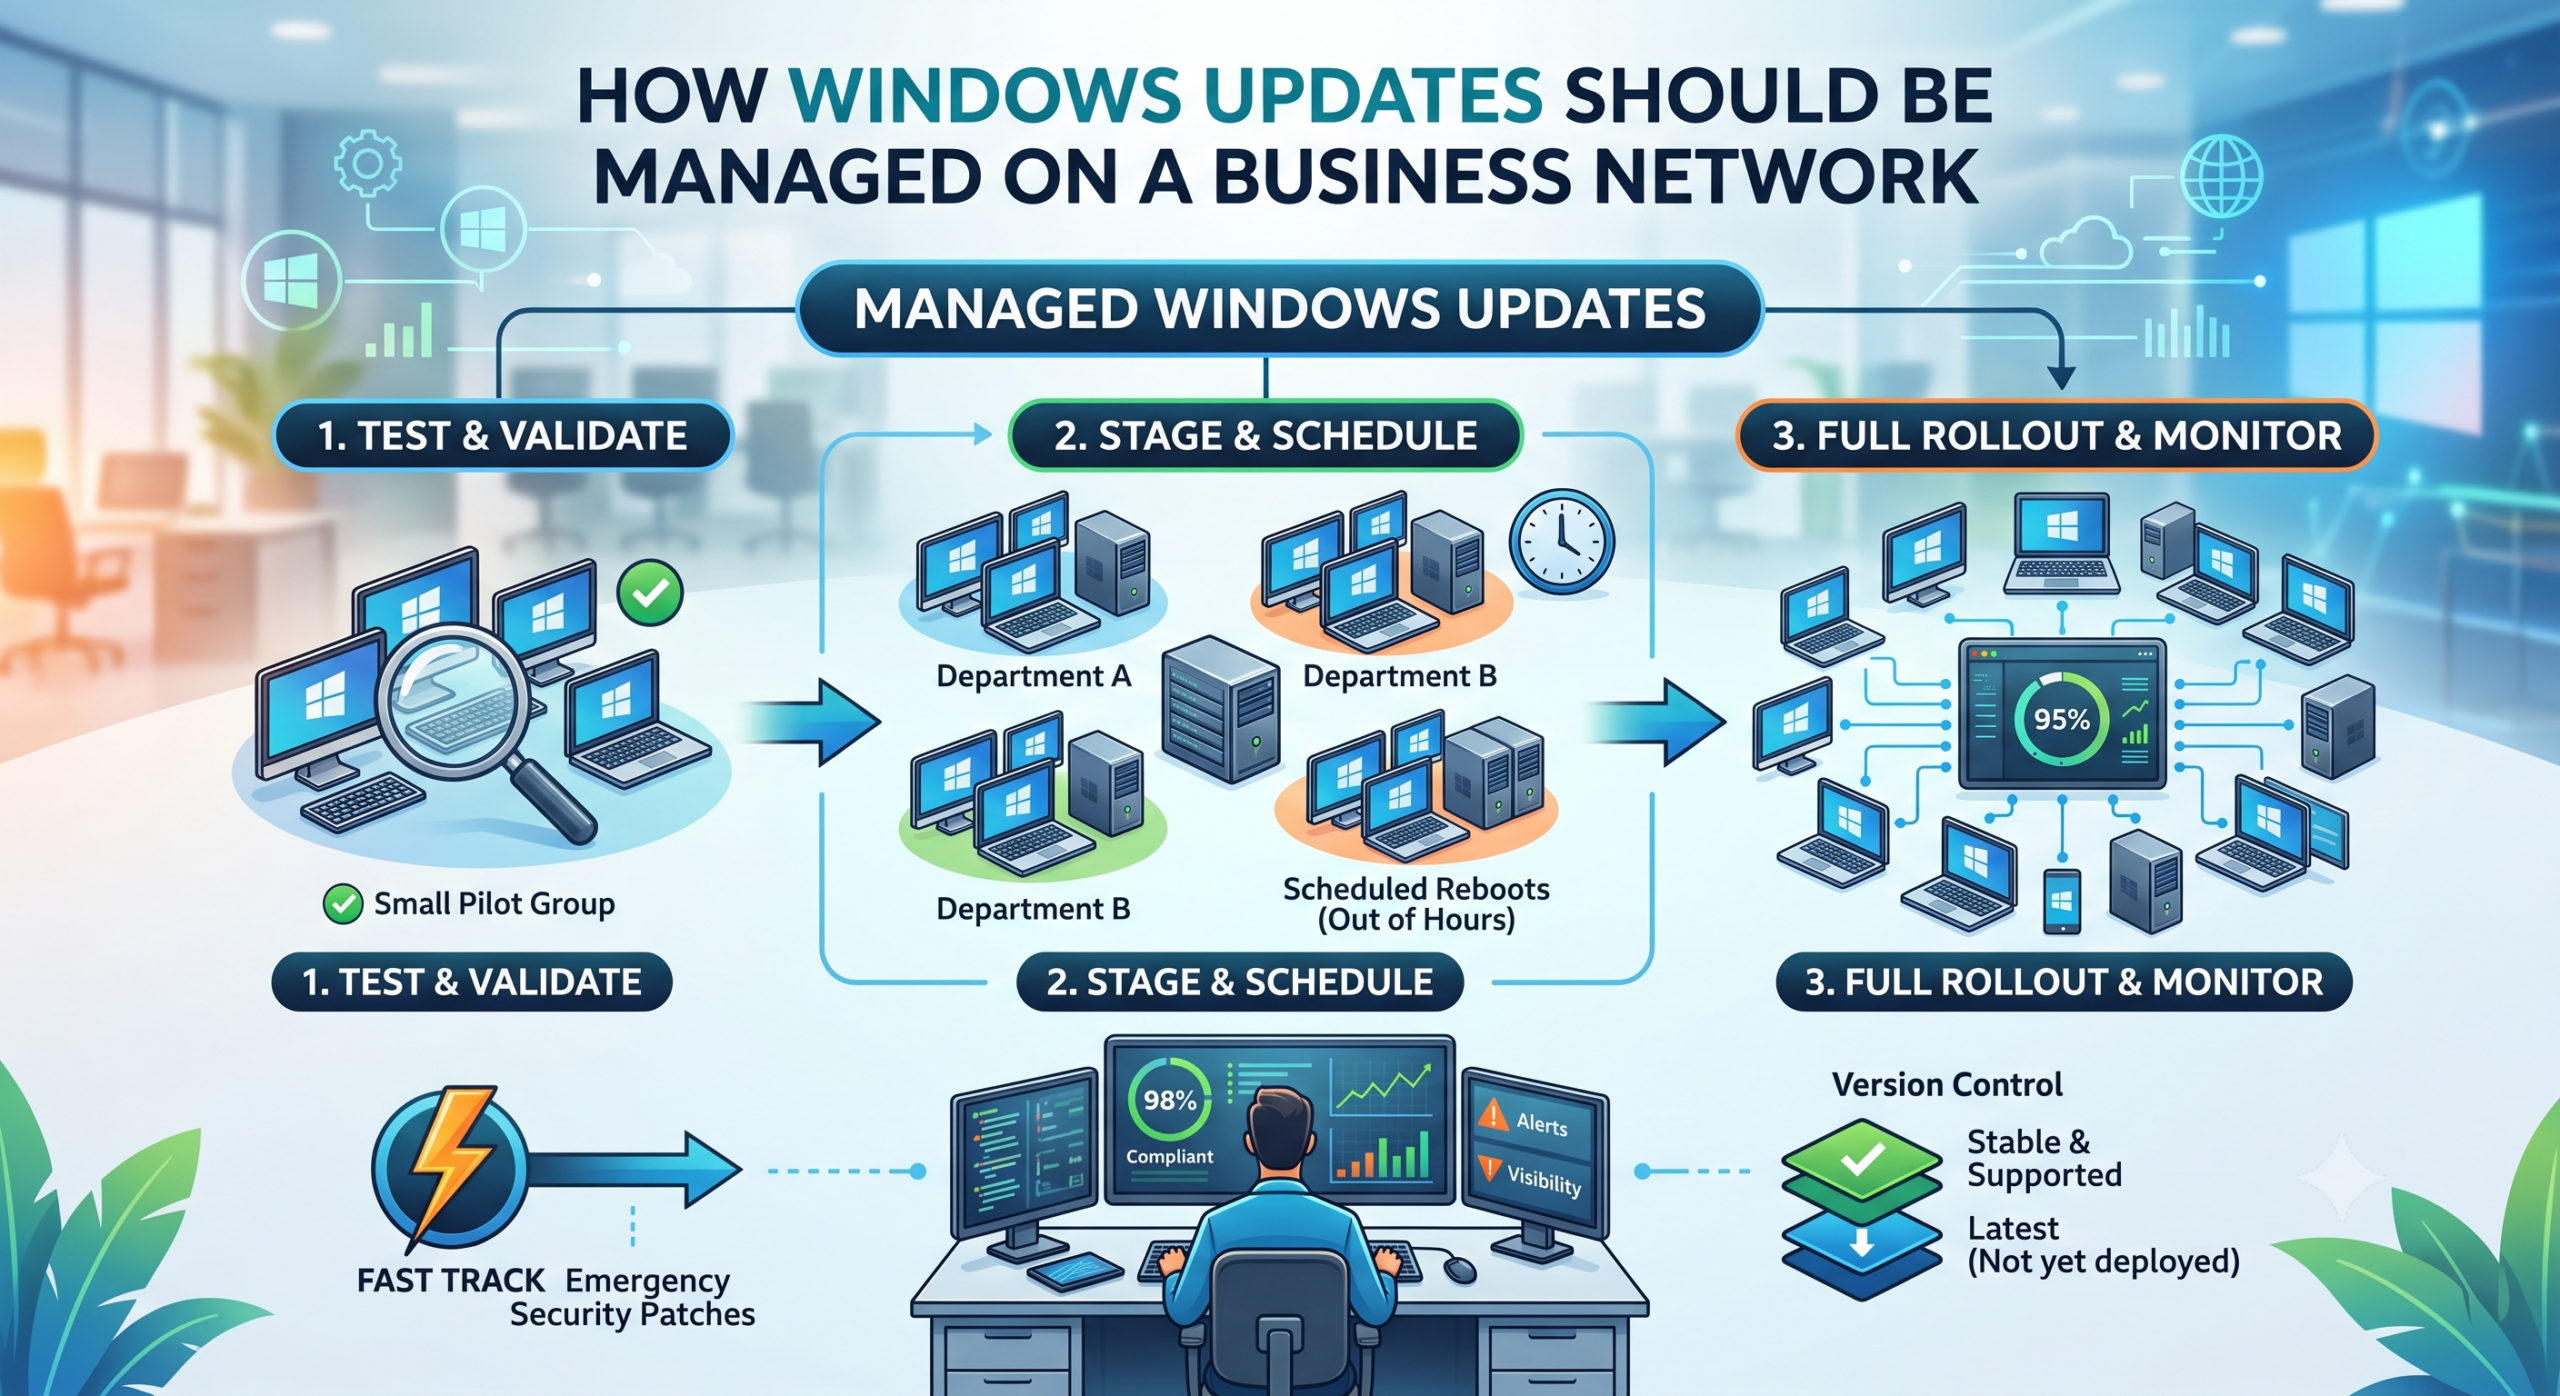
    It doesn’t have to be that way. Managed properly, updates should be something nobody in the business even notices. Here’s what good looks like.

    Test before you trust

    The biggest mistake is pushing every update to every machine the moment Microsoft releases it.

    A better approach is to stage it. Give the update to a small group of machines first, then watch them for a few days. If those are happy, roll it out to everyone else.

    The reason is simple. Bad updates happen, more often than Microsoft would like. If one slips through, you want a couple of machines affected, not the whole company. Staging means you catch it early and stop it before it spreads.

    Think of it as tasting the food before it goes out to the whole table.

    Schedule updates around people, not over them

    Nobody should get a reboot in the middle of a meeting.

    Updates should install and machines restart outside working hours. The work happens quietly in the background and the team gets on with their day.

    Set a deadline too. Without one, people click “remind me later” indefinitely and end up months behind. That gap is exactly where attackers get in.

    Stay on a version that works

    Every so often Microsoft releases a big new version of Windows. Those early releases are usually where the teething problems live.

    Machines shouldn’t leap onto the newest version the day it arrives. Keep the whole business on a stable, supported version, and move up once it’s proven itself. Just don’t leave it so long that you fall out of support and stop getting security fixes. That balance matters.

    Keep a fast lane for serious threats

    The careful, staged approach is right for routine updates. It’s the wrong approach for an emergency.

    When a serious security flaw appears, and one that’s actively being exploited, you need to push the fix out straight away. No staging, no deferral. Good update management has both speeds built in.

    Measure it, don’t assume it

    The part most people skip is checking whether any of it actually worked.

    You need visibility. Something that tells you which machines are up to date and which are lagging. If a machine is stuck, you chase it. Assuming everything’s fine because you set a policy once is how estates quietly drift out of date.

    Scale it to the size of the business

    A large estate can afford several staged groups. A small office of a few PCs can’t, and doesn’t need to.

    For a handful of machines, keep it simple. Update everyone together after a short safety delay. There’s no point building a test group when there aren’t enough machines to have one.

    Match the approach to the size of the business, not the other way round.

    The goal behind all of it is the same. Machines that stay secure and current, with a team that barely notices it happening. If your updates don’t feel like that today, they’re worth a second look.
  • Ghost in the Machine: Fixing the Missing Print Management Console in Windows 11

    Ghost in the Machine: Fixing the Missing Print Management Console in Windows 11

    I was recently setting up a printer deployment for a customer when I realized the Print Management console was nowhere to be found. For IT pros, this tool is essential. It lets you manage printer drivers, ports, queues, and servers all in one place.

    In Windows 11, Microsoft often leaves this feature out by default.

    The good news? It’s still there — you just need to reinstall it.


    Why It’s Missing

    In Windows 11, Print Management is treated as an Optional Feature. If it’s not installed, it simply won’t appear in Administrative Tools or search results.

    Fortunately, adding it back only takes a minute.


    How to Install Print Management in Windows 11

    1. Press Windows Key + I to open Settings.
    2. Click Apps in the left sidebar.
    3. Select Optional features.
    4. Click the blue View features button.
    5. Type Print Management in the search box.
    6. Tick the box.
    7. Click Install.

    Once installed, the console is ready to use.


    How to Launch the Tool Quickly

    Instead of searching through the Start menu, use this shortcut:

    1. Press Windows + R.
    2. Type:
    printmanagement.msc
    
    1. Press Enter.

    This opens the console instantly.


    Why This Tool Is a Lifesaver

    When managing printer deployments for clients, you need visibility. The standard Windows printer settings don’t provide enough detail when:

    • Troubleshooting driver conflicts
    • Cleaning up old print queues
    • Managing ports
    • Deploying printers via Group Policy

    Print Management gives you a clean, centralized view of your entire print infrastructure.

    If you work in IT and haven’t used it in a while, give it another look. It’s still one of the most useful hidden tools in Windows 11.