Category: Intune How-Tos

  • Collect an Autopilot Hardware Hash With PowerShell

    I recently had a rush order of laptops come in from a supplier we don’t normally use. Our usual supplier registers new devices for Autopilot before they ship, but this one didn’t, so I had to collect the hardware hashes myself.

    Here is the PowerShell script I used. It grabs the hash and saves it as a CSV, ready to import into Intune.

    No extra modules, no downloads. It uses what is already built into Windows.

    What the script does

    It reads the hash from the device itself, adds the serial number, and writes a CSV in the format Intune expects.

    You can also add a group tag, which is handy if you sort devices into Autopilot profiles by tag.

    Getting to a desktop from the OOBE

    A brand new laptop sits at the out-of-box experience (OOBE), the first setup screen, with no desktop to run anything from. You can get past it without setting anything up.

    1. At the first OOBE screen, press Ctrl + Shift + F3.
    2. The laptop restarts into audit mode and lands on a desktop, with a System Preparation Tool window open.
    3. Run the script from there (steps below).

    Audit mode signs you in as the built-in administrator, so the script gets the admin rights it needs.

    How to use it

    1. Get the script from my GitHub repo and copy it onto the device, a USB stick works well.
    2. Open PowerShell as administrator. The script will stop with a clear message if you forget.
    3. Run it from the folder where you saved it.
    powershell.exe -NoProfile -ExecutionPolicy Bypass -File .\Get-AutopilotHardwareHash.ps1

    Want a group tag and a specific output path? Add the parameters.

    .\Get-AutopilotHardwareHash.ps1 -GroupTag "Sales" -OutputFile C:\Temp\hwid.csv

    With no parameters, it saves AutopilotHWID.csv in the current folder. Copy the CSV off the device before you carry on.

    Going back to the OOBE

    If you used audit mode, put the laptop back to its first-run state before you hand it on.

    1. In the System Preparation Tool window, set the cleanup action to Enter System Out-of-Box Experience (OOBE).
    2. Leave Generalize unticked.
    3. Set the shutdown option to Reboot and click OK.

    Importing the CSV into Intune

    1. Open the Intune admin center and go to the Windows Autopilot devices page.
    2. Choose Import and select your CSV.
    3. Wait for the import to finish, then check the device appears in the list.

    Imports can take a few minutes, so give it a moment before you panic.

    Good to know

    • It only works on the device you are collecting from, so run it on each one.
    • If the hash is not available, the script tells you rather than saving an empty file.
    • Test it on one device first and check the CSV imports cleanly before you roll it out.

    The script is free to use and change under the MIT licence. Give it a spin and let me know how you get on.

  • Setting up Android Enterprise enrolment in Intune.

    I recently sat down to enrol a fleet of brand new corporate Android tablets into Microsoft Intune.

    Everything was cruising along nicely until Intune stopped me in my tracks with a bizarre error message. What should have been a five minute job turned into a stubborn puzzle that cost me half my morning.

    Picking the Right Enrolment Path

    Before you hand out tablets to a team, you have to tell Intune how they will be used. Android gives you three basic flavours:

    • Corporate-owned, fully managed: The company owns the hardware, one user logs in, and IT has full control. This was what I needed.
    • Dedicated devices: Great for a front desk sign-in screen locked to one app, but useless for mobile staff.
    • Work profile: Best for personal phones where you only want a tiny, secure work bubble.

    I picked fully managed, set up my enrolment profile, and decided to do things properly. For a more detailed explanation of these please visit Android Management Options

    A Quick Win: Naming Your Devices

    Before touching the hardware, I always set up an automatic naming template. Leaving default device names makes your admin portal look like a junk drawer.

    I used this handy format in the enrolment profile:

    TAB-{{DEVICETYPE}}-{{SERIAL}}
    

    This tags every tablet with its hardware type and unique serial number right out of the box. It makes finding a specific device later ridiculously simple.

    Down the Rabbit Hole

    Next, I wanted every new tablet to drop into a dedicated Entra ID security group automatically as soon as it enrolled. That way, all the apps and security policies apply without me lifting a finger.

    I tried to save the profile, but Intune threw a giant warning at me:

    “Before you configure device groups, make sure that the Intune Provisioning Client or Intune ClientConfidential app has been added as an owner.”

    Fair enough, I thought. I jumped over to Entra ID, opened my tablet security group, clicked Owners, and searched for both names.

    Nothing. The search box stared back at me, completely blank.

    I figured the app was just hiding in the tenant. I opened Enterprise applications and searched for “Intune”, but the only thing that popped up was a PowerShell tool. Neither of the apps Microsoft explicitly told me to add actually existed under those names.

    Cracking the Code

    After twenty minutes of digging through documentation and banging my head against the desk, I realised Microsoft played a naming trick. The service principal is in your tenant, but its display name changes depending on how the tenant was set up.

    The name is a red herring. The secret is finding it by its permanent Application ID:

    f1346770-5b25-470b-88bd-d5744ab7952c
    

    Once I stopped searching for names, fixing it took sixty seconds:

    1. Open Entra ID and head to Enterprise applications.
    2. Change the search filter to Application ID starts with and paste in f1346770-5b25-470b-88bd-d5744ab7952c.
    3. Check the name that appears. In my tenant, it was disguised as Intune Autopilot ConfidentialClient.
    4. Go back to your device group, click Owners, choose Add owners, and paste that exact name in.

    As soon as that hidden app became an owner, Intune happily accepted the group and the tablets enrolled smoothly.

    Save that Application ID in your notes. The next time Intune sends you on a wild goose chase, you can skip the headache and get right back to work.

    Give it a spin on your next rollout and see what you think.

  • Adding Your First MacBook to Intune: A Step-by-Step Guide

    One of our customers had purchased a few MacBook Air laptops last week and were keen to get them up and running. I suggested that we at least get them enrolled in Intune with a very basic config before they go out in the field. Here are the steps I took to get them out the door.

    Mac enrolment in Intune isn’t complicated once you’ve done it once. The tricky part is knowing which route to take before you start, because Apple gives you two very different paths depending on how the device was bought.

    This guide covers both: Automated Device Enrolment (ADE) for a corporate-owned Mac bought through Apple Business Manager, and Company Portal enrolment for anything else. If you followed my earlier post on connecting Apple Business Manager to Intune for iOS, the ABM/MDM server link-up is already done. This is the same server, just adding Macs to it.

    Which route do you need?

    ADE (zero-touch) — the Mac was purchased through Apple Business Manager, or added to ABM via Apple Configurator. It shows up in Devices in ABM already. This is the route for corporate-owned kit and gives you a fully managed device from first boot.

    Company Portal (user-driven) — the Mac wasn’t bought through ABM, or it’s a personal/BYOD device. The user installs Company Portal themselves and enrols manually. Less control (no Setup Assistant automation, user can technically unenrol), but it works on any Mac.

    If you’re not sure which one you need, check Apple Business Manager under Devices first. If it’s listed there, use ADE.

    Prerequisites

    Before you start, confirm:

     Apple Business Manager is linked to your Intune tenant (Devices > Enrollment devices > Enrollment Program Tokens in Intune)

     The Mac is assigned to your MDM server in ABM, if you’re using ADE

     You have a macOS enrolment profile configured in Intune (Devices > macOS > Enrollment > Enrollment profiles)

     The user has an Intune licence assigned

    Skip any of these and enrolment will either fail outright or leave the device half-configured.

    Route 1: Automated Device Enrolment (ADE)

    1. Assign the device to your MDM server in Apple Business Manager

    Log into ABM, go to Devices, find the Mac by serial number, and assign it to the Intune MDM server. If it was bought directly through Apple with your ABM account linked, this happens automatically. If it came from a reseller, you may need to do this manually or ask the reseller to push it through.

    2. Create or check your enrolment profile in Intune

    Go to Devices > macOS > Enrollment > Enrollment Program Tokens, select your token, and open Profiles. Create a profile if you don’t have one:

     Set authentication method (usually Setup Assistant with modern authentication)

     Decide which Setup Assistant screens to skip (Location Services, Siri, and Apple ID are common ones to hide for corporate builds)

     Enable “Await final configuration” if you want the device to stay locked to a Configuration screen until all app and profile pushes finish. Worth turning on if first-boot policy delivery has ever been patchy in your tenant.

    3. Assign the profile to the device

    Back in the device list under your token, select the Mac and assign the profile you just built. This can take a few minutes to sync from Apple’s side, so don’t panic if it’s not instant.

    4. Boot the Mac

    Power it on (or factory reset if it’s been used before — ADE only triggers on a clean Setup Assistant run). The device will check in with Apple, pull down the MDM enrolment, and the user will be guided through Setup Assistant with your configured screens. No Apple ID sign-in prompt, no manual profile installation.

    5. Confirm enrolment in Intune

    Once through Setup Assistant, the device should appear in Devices > All devices within a few minutes, with compliance and configuration policies starting to apply. Check Managed Apps and Compliance status to confirm policies are actually landing, not just that the device shows up.

    Route 2: Company Portal (user-driven)

    1. Install Company Portal

    Download the ⁠.pkg⁠ installer directly from Microsoft by navigating to ⁠aka.ms/EnrollMyMac⁠ or by logging into the Intune Company Portal website. The macOS Company Portal app is not distributed through the Mac App Store.

    2. Sign in

    Open Company Portal and sign in with the user’s work account. It’ll prompt to enrol the device — accept.

    3. Download and install the management profile

    Company Portal generates a management profile the user needs to download and install manually through System Settings > Profiles. This is the one extra step ADE skips, and the one most users get stuck on, so it’s worth walking them through it the first time.

    4. Confirm enrolment

    Once the profile installs, Company Portal shows the device as enrolled, and it’ll appear in Intune within a few minutes same as the ADE route.

    A few things that catch people out

     ADE only fires on Setup Assistant. If the Mac has already been through first-time setup, you need to wipe it (or use Apple Configurator to force a factory-style reset) before ADE will apply. You can’t “convert” a live device to ADE enrolment after the fact.

     Token expiry. ABM enrolment tokens expire annually. If devices stop showing up under your token in Intune with no obvious cause, check the token hasn’t lapsed first.

     Await final configuration can backfire if your policies aren’t fully sorted, because the device sits on the lock screen until everything’s pushed. Test with one device before rolling it out to a batch.

     Company Portal enrolment isn’t as sticky. A user can remove the management profile from System Settings unless you’ve layered in additional restrictions. Fine for BYOD, not something I’d rely on for a fully corporate-managed Mac.

    Once you’ve got one Mac through either route, the rest of the fleet follows the same pattern. The main thing worth getting right early is deciding ADE vs Company Portal per device before it lands on a desk, since switching from one to the other later means a rebuild.
  • Which Android Management Mode Do You Actually Need?

    I spent way too much time testing different Android enterprise setups before realizing one simple truth: you cannot manage every device the same way.

    Pick the wrong mode, and you either end up with angry staff or a massive security headache.

    Here is how I break down the three main flavors of Android device management, so you can pick the right tool for the job.

    Corporate-Owned, Fully Managed

    The company buys the phone, hands it to an employee, and IT keeps full control.

    This was exactly what I needed for my fleet. You can push updates, wipe the hardware remotely if it gets lost, and lock down security settings without asking permission.

    • Best for: Company-owned phones issued to individual staff members.
    • Why it works: You get complete visibility and protection without compromise.

    Dedicated Devices

    Think of these as digital kiosks. They are locked down tight, usually running just a single app or a tiny set of approved tools.

    They are fantastic for a front-desk visitor sign-in screen, a warehouse barcode scanner, or an interactive shop display. But try giving one to a mobile worker who needs email, maps, and a browser, and it quickly becomes useless.

    • Best for: Kiosks, shared inventory scanners, and point-of-sale tablets.
    • Why it works: Nobody can tamper with the settings or wander off into YouTube.

    Work Profile

    This is the sweet spot for Bring Your Own Device (BYOD) setups.

    Instead of taking over the entire phone, you create a secure, encrypted sandbox just for company apps like email and Slack. The user keeps total privacy on their side of the phone, and IT gets full control inside the work container. If that person leaves the company, you can wipe the work data in one click without touching their personal family photos.

    • Best for: Personal phones used for light day-to-day work tasks.
    • Why it works: Total privacy for the employee, solid security for the company.

    Match the management mode to the actual daily job, and your deployment will run a whole lot smoother. Give these setups a test run in your lab and see which one fits your team best.

  • Demystifying the Intune Remove Data Menu

    I used to stare at the device actions menu in Intune and panic. I was always terrified of clicking the wrong button and accidentally deleting a user’s personal photos. Microsoft recently updated the admin center interface to tidily group all these reset options into one neat “Remove data” menu. It looks a lot cleaner now. If you are still a bit confused by the four different choices, you are definitely not alone.

    Here is exactly what each button actually does.

    • Retire: This removes company data and unhooks the device from your management. It leaves personal apps and files completely untouched. This is the polite choice for a departing employee who is keeping their own device.
    • Wipe: It performs a full factory reset and deletes all personal and company data. You should use this strictly for lost, stolen, or entirely decommissioned company hardware.
    • Fresh start: Think of this as a deep clean for the operating system. It reinstalls a fresh copy of Windows and removes annoying manufacturer bloatware. The device stays enrolled in your system.
    • Autopilot Reset: This gets a machine perfectly ready for its next owner. It wipes the previous user’s data and settings. The computer stays fully enrolled and ready to hand straight to the new employee.

    Here is my quick cheat sheet to help you remember the differences.

    1. Retire: Unmanage the device but protect personal data.
    2. Wipe: Delete absolutely everything.
    3. Fresh start: Clean up the operating system but keep it enrolled.
    4. Autopilot reset: Prep for the next user without re-enrolling.

    Hopefully, this saves you from a mild panic attack the next time you need to clear a device. Give it a spin and see what you think.

  • Linking Apple Business Manager with Microsoft Intune

    Linking Apple Business Manager with Microsoft Intune

    Today I had I continue configuring the iPad for a customer now that the Apple Buainess account had been approved. Since this was the first corporate owned Apple device they had purchased and wanted managed. I needed to connect Intune to Apple Business Here is the second part to the managing apple devices in Intune.

    If Intune is your MDM and you’re deploying Apple kit at scale, Apple Business and Intune need to be talking to each other before a single corporate iPhone, iPad, or Mac goes out the door.

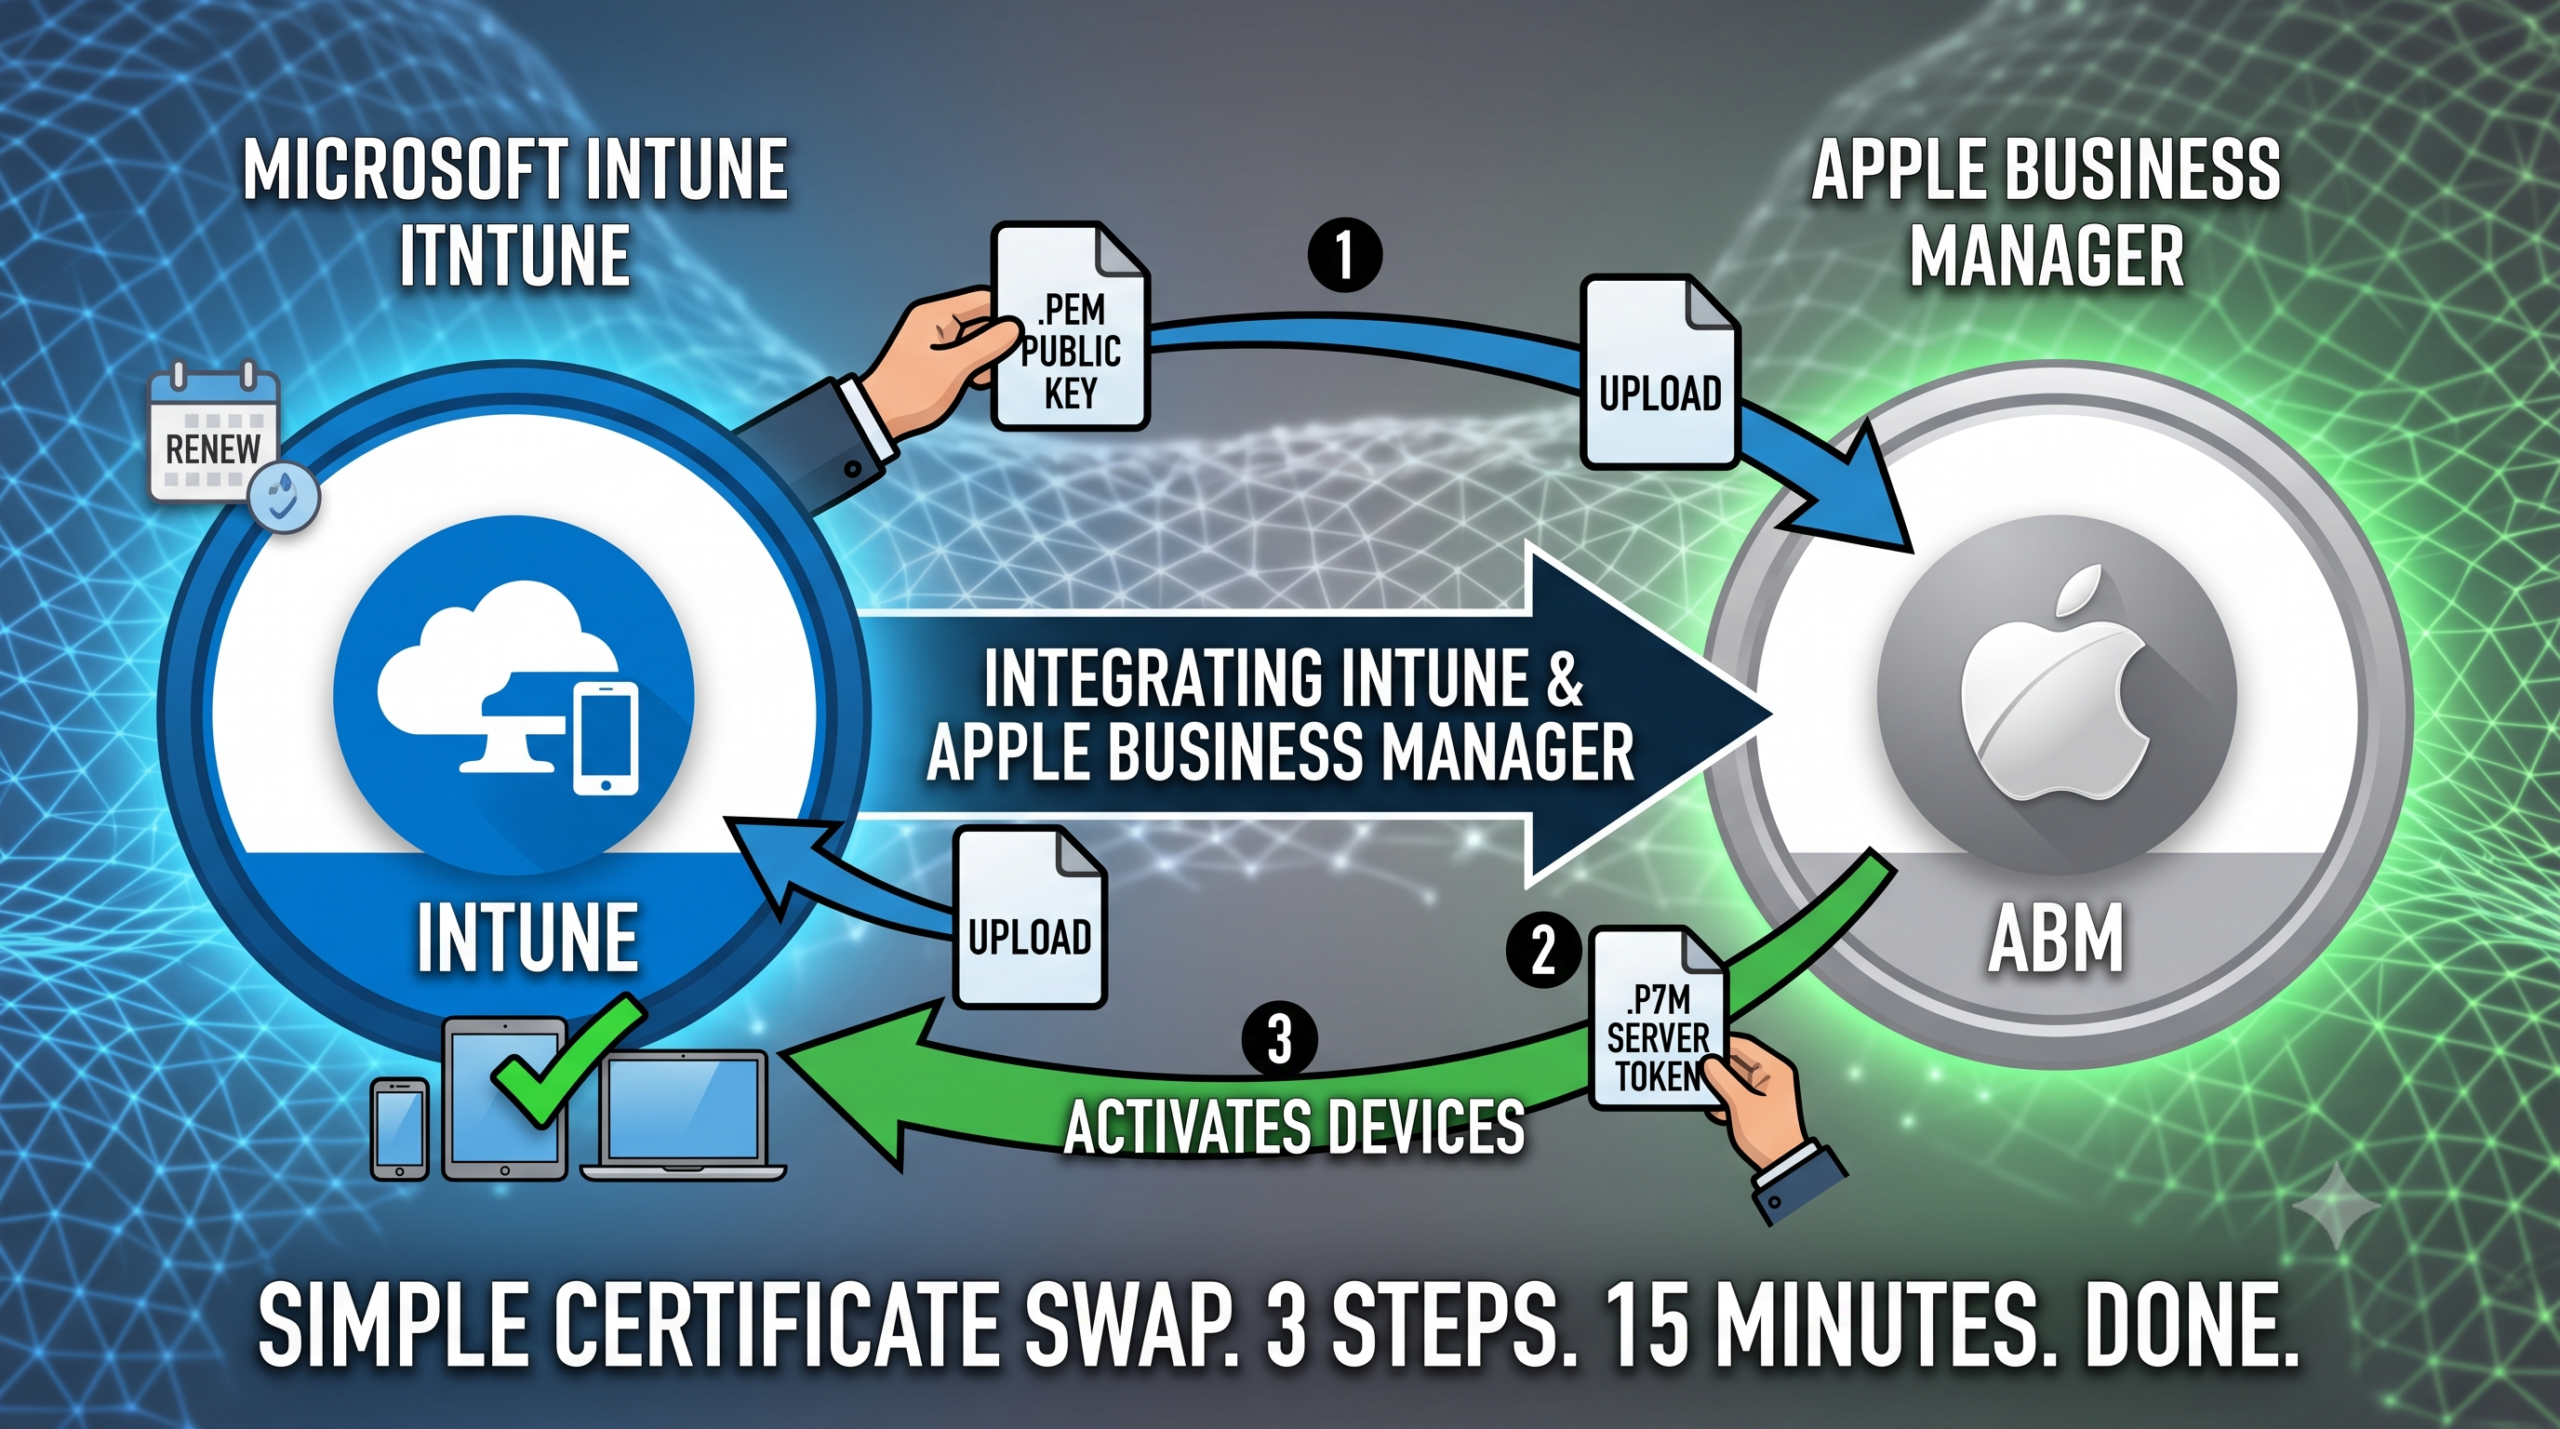
    People overthink this integration. It’s a certificate swap. Pull a public key from Intune, hand it to Apple, bring Apple’s token back home. Three steps, fifteen minutes, done.

    Here’s how to set it up.

    Phase 1: Grab the public key from Intune

    You’re generating an encryption key in your tenant so Apple knows who it’s trusting.

    1. Sign in to the Microsoft Intune admin center.
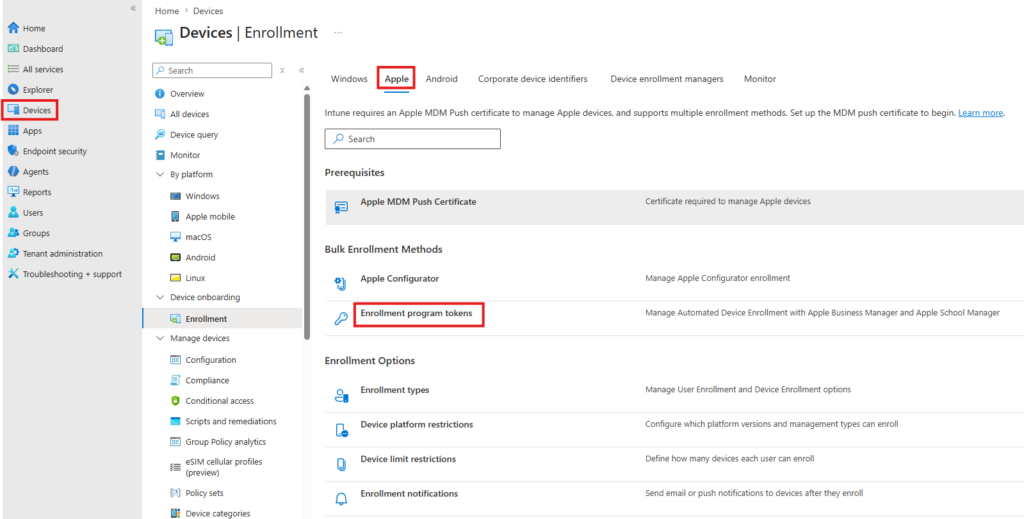
    2. Go to Devices > Enrollment (under Device onboarding) > Apple.
    3. Select Enrollment program tokens and click Create.
    4. Tick the box agreeing to let Microsoft send user and device info to Apple.
    5. Click Download your public key — this grabs the .pem certificate.
    6. Keep this tab open. You’ll need it again in a minute.

    Phase 2: Build the MDM server in Apple Business

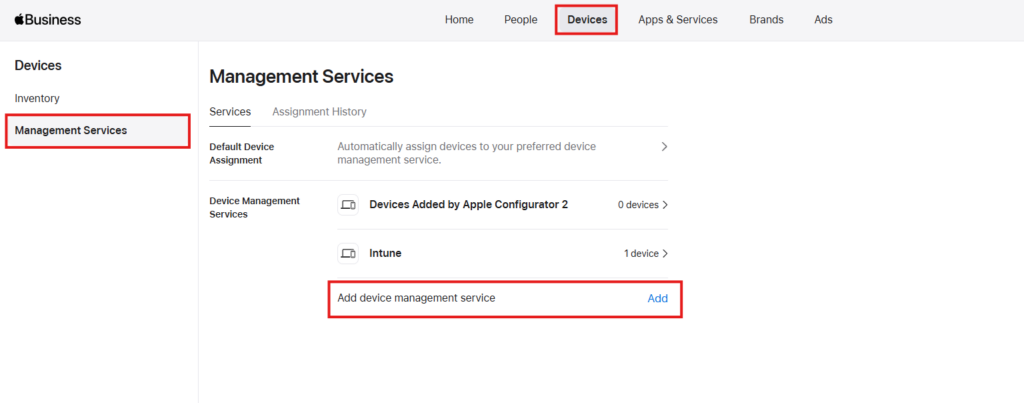
    Open a new tab and log in to Apple Business. https://business.apple.com/ You’ll need the Administrator or Device Enrollment Manager role.

    At the top select Devices, click your Management Services, then Add device management service click Add.

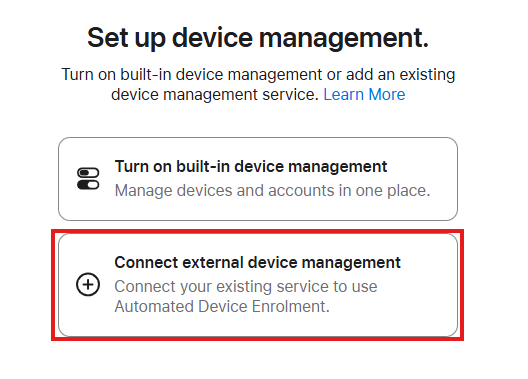
    Under Set up device management, select Connect to external device management, then click the continue button at the bottom.

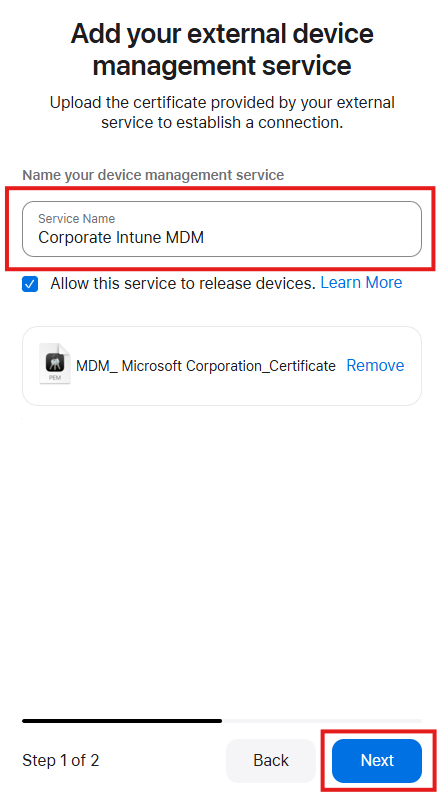
    Give it a sensible name — “Corporate Intune MDM” does the job.

    Under MDM Server Settings, upload the .pem file from Phase 1, and click the blue Next button

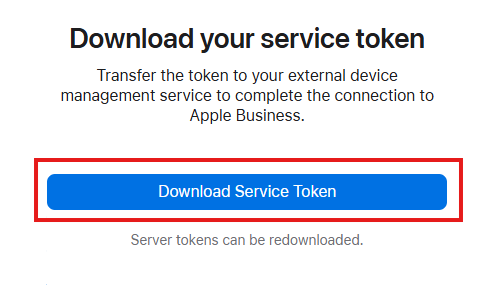
    Click Download Service token. and click Done.

    Phase 3: Upload Apple’s token back into Intune

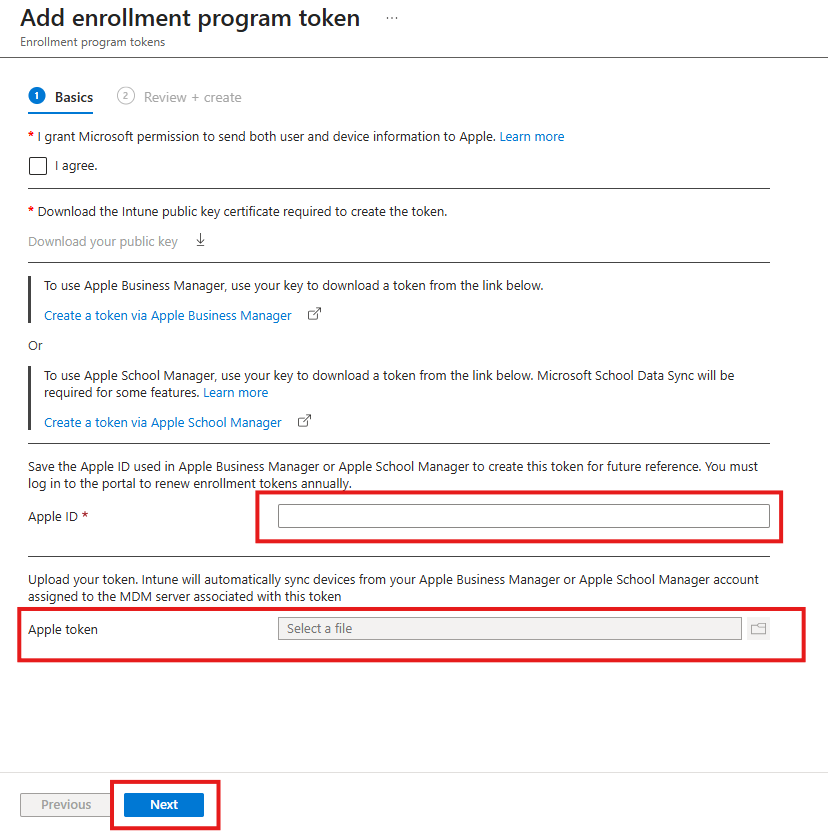
    1. Back to your Intune tab.
    2. In the Apple ID box, enter the corporate Apple ID tied to your ABM account. Worth a comment here for whoever inherits this tenant down the line — they’ll want to know which Apple ID this is.
    3. In the Apple token box, upload the .p7m file from Apple.
    4. Click Next to skip past scope tags (unless your org actually uses them), then Create.

    What happens next

    Token status flips to Active and the plumbing’s in place. Two jobs left:

    Assign hardware in Apple Business. Head to Devices, find your serial numbers or order numbers, assign them to the Intune MDM server you just created.

    Sync and build profiles in Intune. Back to your enrollment token settings, hit Sync to pull the newly assigned serials through. Once they show up, build your Enrollment Program Profiles — force supervision, lock the MDM profile, skip the setup assistant screens for the end user.

    One thing to flag for future you: these tokens expire annually. Stick a reminder in the calendar now, or you’ll be doing this again in a panic next year.